Fixes#345. CI's npm audit --audit-level=high --omit=dev step started failing on every branch (it's what blocks #344) after new advisories were published.
package
from → to
advisory
how
source-map-js
1.2.1 → 1.2.2
GHSA-68fv-2mgg-jv7q (high, event-loop DoS)
transitive (sanitize-html → postcss), in range, lockfile only
i18next-http-backend
4.0.0 → 4.0.2
GHSA-xvq9-wjp8-hwqf (low, URL validation)
pinned patch bump
katex
0.16.47 → 0.18.11
GHSA-238p-pmpm-9mq7 (low, prototype pollution vs trust)
first fixed in 0.18.2
katex 0.17/0.18 breaking changes: an internal __defineFunction API and prefixed internal CSS classes. Lotus uses neither: KaTeX.tsx calls renderToString with fixed options and imports the package's own stylesheet. 0.19 wasn't needed.
The lockfile changes only those packages, plus katex's own CLI dependency commander 8 → 15. npm audit --omit=dev: 0 vulnerabilities.
Verified (headless Chromium against Vite with a fresh dep cache; 0.18.11 confirmed served):
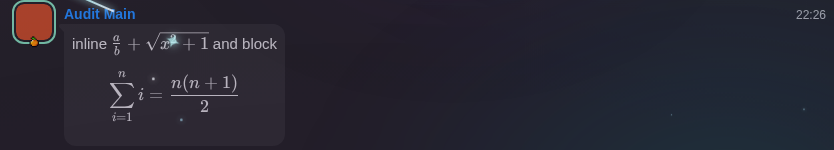
inline and display math render (\frac, \sqrt, \sum with limits);
KaTeX fonts load;
no page errors;
translations still load (English strings, no raw keys).
tsc clean · unit tests 1319 pass / 2 skipped · ESLint 0 errors (36 warnings, unchanged) · Prettier clean · production build OK.
Fixes #345. CI's `npm audit --audit-level=high --omit=dev` step started failing on every branch (it's what blocks #344) after new advisories were published.
| package | from → to | advisory | how |
|---|---|---|---|
| source-map-js | 1.2.1 → 1.2.2 | GHSA-68fv-2mgg-jv7q (**high**, event-loop DoS) | transitive (sanitize-html → postcss), in range, lockfile only |
| i18next-http-backend | 4.0.0 → 4.0.2 | GHSA-xvq9-wjp8-hwqf (low, URL validation) | pinned patch bump |
| katex | 0.16.47 → 0.18.11 | GHSA-238p-pmpm-9mq7 (low, prototype pollution vs `trust`) | first fixed in 0.18.2 |
**katex 0.17/0.18 breaking changes:** an internal `__defineFunction` API and prefixed internal CSS classes. Lotus uses neither: `KaTeX.tsx` calls `renderToString` with fixed options and imports the package's own stylesheet. 0.19 wasn't needed.
The lockfile changes only those packages, plus katex's own CLI dependency `commander` 8 → 15. `npm audit --omit=dev`: **0 vulnerabilities**.
**Verified** (headless Chromium against Vite with a fresh dep cache; 0.18.11 confirmed served):
- inline and display math render (`\frac`, `\sqrt`, `\sum` with limits);
- KaTeX fonts load;
- no page errors;
- translations still load (English strings, no raw keys).
`tsc` clean · unit tests 1319 pass / 2 skipped · ESLint 0 errors (36 warnings, unchanged) · Prettier clean · production build OK.
🤖 Generated with [Claude Code](https://claude.com/claude-code)
https://claude.ai/code/session_01PPmy3tPq869XDW4njjVaKA
`npm audit --audit-level=high --omit=dev` (Build & Quality Checks) started
failing on every branch after new advisories were published:
- source-map-js 1.2.1 → 1.2.2 (high, GHSA-68fv-2mgg-jv7q; transitive via
sanitize-html → postcss, in range — lockfile only)
- i18next-http-backend 4.0.0 → 4.0.2 (low, GHSA-xvq9-wjp8-hwqf)
- katex 0.16.47 → 0.18.11 (low, GHSA-238p-pmpm-9mq7; fixed in 0.18.2).
0.17/0.18's breaking changes are an internal __defineFunction API and
prefixed internal CSS classes; Lotus uses neither (KaTeX.tsx calls
renderToString and imports the package's own stylesheet).
Only these four lockfile entries change (plus katex's own CLI dependency
commander 8 → 15). npm audit --omit=dev: 0 vulnerabilities.
Verified headless against Vite with a fresh dep cache (katex 0.18.11
served): inline and display math render (\frac, \sqrt, \sum with limits),
KaTeX fonts load, no page errors; translations still load (en strings,
no raw keys). tsc clean, 1319 unit tests pass, eslint 0 errors (36
warnings, unchanged), prettier clean, production build OK.
Fixes#345
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
Claude-Session: https://claude.ai/code/session_01PPmy3tPq869XDW4njjVaKA
Blocking a user prevents them from interacting with repositories, such as opening or commenting on pull requests or issues. Learn more about blocking a user.


Fixes #345. CI's
npm audit --audit-level=high --omit=devstep started failing on every branch (it's what blocks #344) after new advisories were published.trust)katex 0.17/0.18 breaking changes: an internal
__defineFunctionAPI and prefixed internal CSS classes. Lotus uses neither:KaTeX.tsxcallsrenderToStringwith fixed options and imports the package's own stylesheet. 0.19 wasn't needed.The lockfile changes only those packages, plus katex's own CLI dependency
commander8 → 15.npm audit --omit=dev: 0 vulnerabilities.Verified (headless Chromium against Vite with a fresh dep cache; 0.18.11 confirmed served):
\frac,\sqrt,\sumwith limits);tscclean · unit tests 1319 pass / 2 skipped · ESLint 0 errors (36 warnings, unchanged) · Prettier clean · production build OK.🤖 Generated with Claude Code
https://claude.ai/code/session_01PPmy3tPq869XDW4njjVaKA